01 // CUSTOM
Customizable WAF
Domain-based patterns let you set security levels per website. Tune filters for each domain on the server instead of forcing one policy on every site.
Try now →
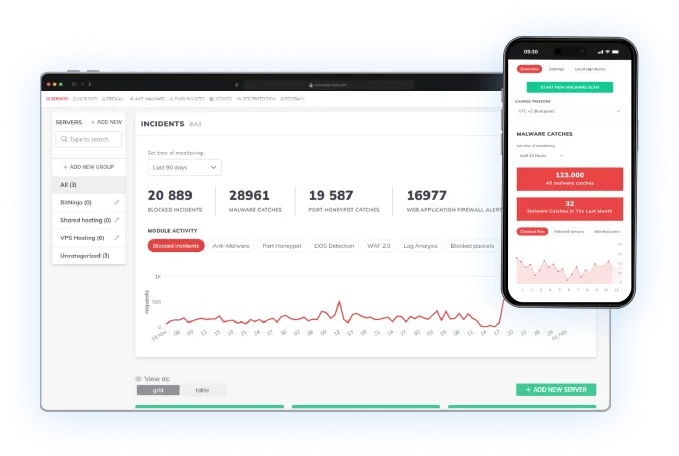
BitNinja WAF inspects HTTP traffic and blocks malicious requests before they reach websites on your servers. It filters SQL injection, XSS, CMS exploits and other suspicious web requests. Designed for hosting providers, server administrators and infrastructure operators.
[ no credit card · 7-day full arsenal ]
sys://waf
Activate the WAF module and keep CMS traffic filtered without the ops overhead.
01
Central configuration with per-domain filter adjustments, built for shared server fleets.
02
Continuously updated rules for emerging CMS threats, with a low false-positive rate.
03
Auto-rejects suspicious web requests so attacks never reach the application.
sys://definition
A Web Application Firewall (WAF) analyzes web and HTTP traffic and blocks malicious requests before they reach the protected website or web application. It inspects incoming requests against security rules, then lets legitimate traffic through. BitNinja WAF applies that website firewall on Linux web servers so hosting providers and sysadmins can protect many sites from one place.
sys://coverage
BitNinja WAF stops SQL injection, Cross-Site Scripting (XSS), CMS exploits and other malicious HTTP requests before they reach the application.
01
Blocks requests that try to manipulate databases through the web application.
02
Filters requests that attempt to inject malicious scripts into websites.
03
Applies rules for common CMS vulnerabilities on hosted websites.
04
Rejects suspicious web traffic that does not belong in a legitimate request.
sys://waf-pipeline
BitNinja WAF inspects incoming HTTP requests against cloud-updated rules, blocks malicious traffic, and forwards legitimate requests to the website or application.
01
HTTP and HTTPS requests to hosted sites hit BitNinja WAF first.
02
The WAF examines each request against its ruleset. It runs as a standalone engine, so it does not depend on Apache, NGINX or LiteSpeed modules.
03
Cloud-updated rules, including CMS-specific patterns, evaluate the request in real time.
04
Requests that match attack patterns are rejected automatically.
05
Clean requests continue to the website, so legitimate visitors are not interrupted.
sys://waf-depth
Per-domain controls, CMS-focused rules, and less wasted work on the origin.
01 // CUSTOM
Domain-based patterns let you set security levels per website. Tune filters for each domain on the server instead of forcing one policy on every site.
Try now →02 // CMS
Custom WAF rules cover WordPress, Joomla, Drupal and more, and update as new vulnerabilities appear. That keeps common hosted CMS stacks protected at the request layer.
Start free trial →03 // SSL
Blocking malicious requests before they reach applications reduces unnecessary work on the web server. SSL terminating also offloads HTTPS connections, with no prior setup required.
Reduce server load →sys://hosting
BitNinja WAF is a web application firewall for hosting providers: one module on the Linux server, many websites, and central management.
01
It fits environments that host many domains on shared Linux servers, not only a single application.
Shared hosting security →02
Filter adjustments and security levels can be set per domain from the same central configuration.
03
Proactive blocking and a low false-positive rate mean fewer junk requests hitting customer sites.
sys://cms
BitNinja WAF includes rules for the CMS platforms most often hosted on Linux servers: WordPress, Joomla and Drupal.
sys://user-signal
“The whole platform is feature-rich, especially with the WAF module. It has everything that a web hosting company or sysadmin needs.”
sys://faq
WAF protection, CMS coverage, per-domain controls and hosting fit.
A Web Application Firewall (WAF) analyzes HTTP traffic and blocks malicious requests before they reach a website or web application. BitNinja WAF does this on the Linux server, in front of the hosted sites.
It inspects each incoming web request against security rules, then blocks matches and forwards the rest to the application. BitNinja WAF does this in real time with cloud-updated rules.
BitNinja WAF can block SQL injection, Cross-Site Scripting (XSS), CMS exploits and other malicious HTTP requests. Suspicious requests are rejected before they reach the application.
Yes. It includes WAF rules for WordPress, Joomla, Drupal and more. Those rules update as new CMS vulnerabilities appear.
Yes. Domain-based patterns let you set security levels and filter adjustments per website. Configuration stays central, with per-domain control for shared servers.
Yes. It is aimed at hosting providers, server administrators and infrastructure operators. One module covers many sites on a shared server without a separate WAF product per domain.
[ full arsenal · no limitations ]
Don't worry. The installation process is quick and straightforward.
[ No credit card required ]