2026-11-02 · 3 min · Gyula Hosszú
PolyShell: Block Upload, Execution and Backdoor Access with WAF Rules
BitNinja has released three WAF rules to block DeepVeinDrilling backdoor access, Polyshell PHP exec from media and malicious file upload
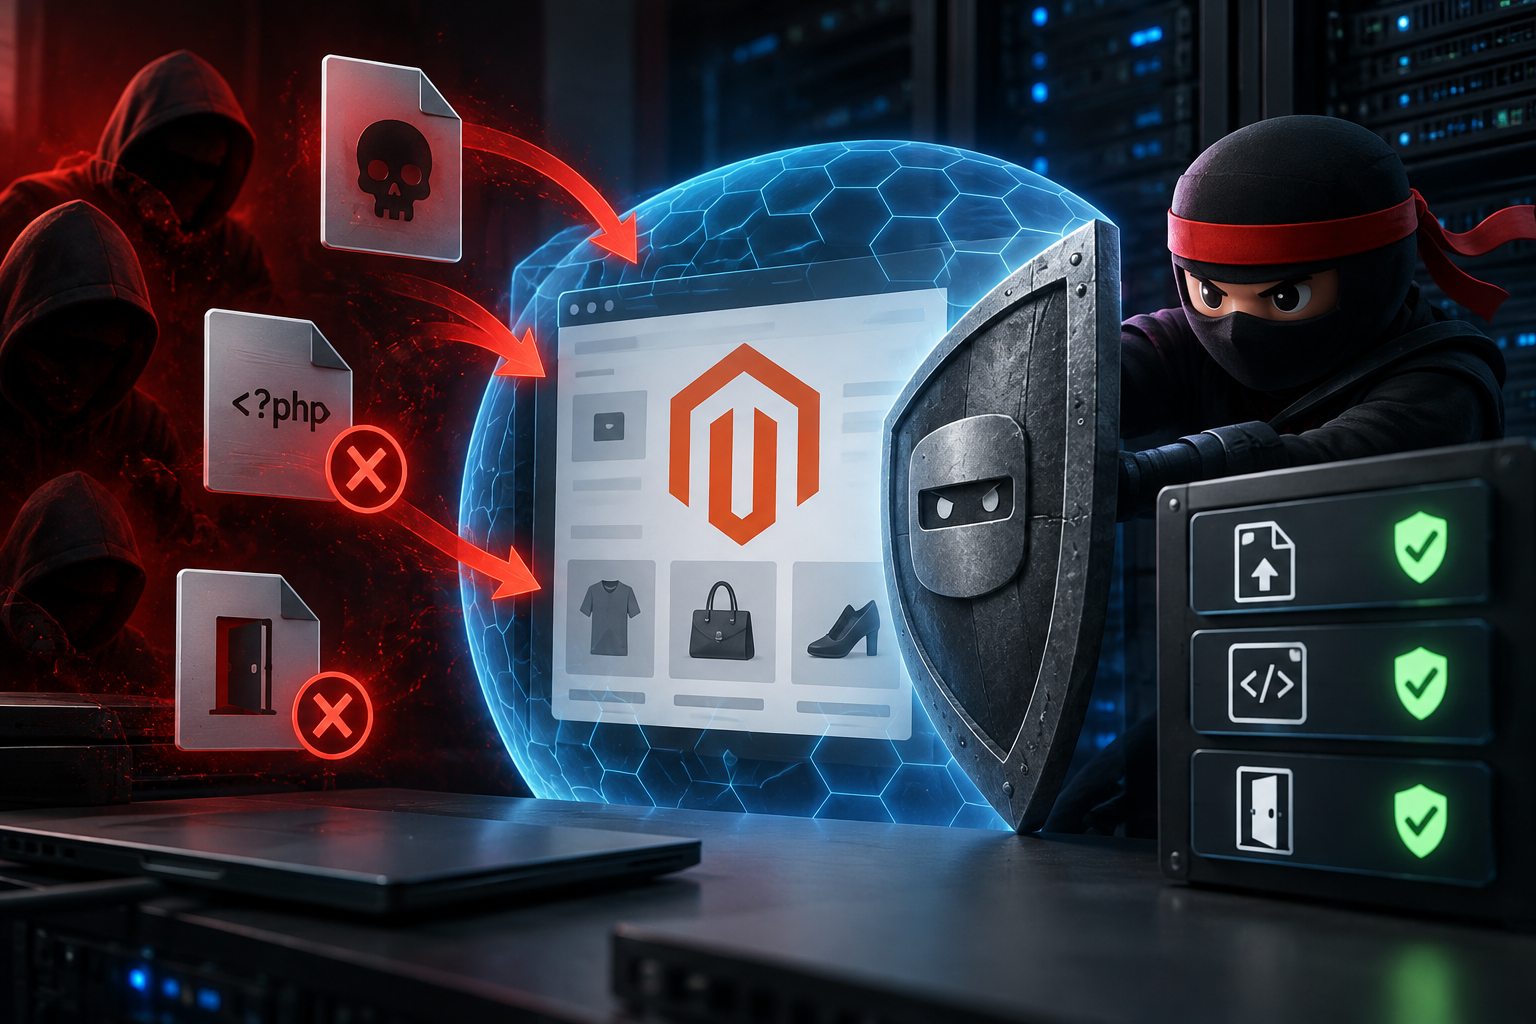
Patched Magento stores can still be compromised
CVE-2026-48356, known as PolyShell, is an actively exploited file-upload flaw affecting Magento Open Source and Adobe Commerce versions 2.4.4 through 2.4.9, along with B2B versions 1.3.3 through 1.5.3. Adobe fixed the issue in its July release, APSB26-73.
The vulnerability has a CVSS score of 9.3. CISA has added it to the Known Exploited Vulnerabilities catalog, and Sansec observed 471 stores being exploited within one hour.
The attack does not require authentication. An attacker abuses the guest cart API endpoint:
/V1/guest-carts/{cartId}/items
The request uploads a PHP shell disguised as a GIF image. The file is placed in a Magento media directory, typically under pub/media/custom_options/quote/. If the server permits PHP execution from media folders, the uploaded shell can run.
That gives the attacker a foothold for payment-card theft and further changes to the store.
DeepVeinDrilling keeps patched stores exposed
PolyShell is also used in the DeepVeinDrilling card-skimming campaign, which has affected 953 stores. The campaign plants an accesson.php backdoor in assets/images/ and hides a JavaScript loader in a Magento cms_block.
This creates a problem for stores that have already applied the Adobe fix. Patching closes the original vulnerability, but it does not remove a shell or clean malicious content that was added before the patch. A store can therefore remain compromised and be reinfected or continue sending payment data to an attacker.
Three new BitNinja WAF rules
BitNinja has released three rules for Web Application Firewall modules. Together, they interrupt the attack at three points:
-
Malicious guest-cart uploads
The first rule blocks uploads through the guest-cart REST endpoint when the
file_infofield contains executable extensions such as.php,.phtml, or.phar. It also covers JSON and Unicode-escaped variants. -
PHP execution in Magento media folders
The second rule blocks PHP files executed from Magento media upload directories, including
custom_optionsandcustomer_address. -
The known backdoor path
The third rule blocks requests to
assets/images/accesson.php, the known DeepVeinDrilling backdoor path.
For hosting providers, server-level filtering gives unpatched Magento accounts immediate protection while customers work through their update schedule. It also adds coverage for the backdoor and execution stages, which a software update alone does not address.
Recommended actions for server owners
Apply the following steps on affected Magento and Adobe Commerce servers:
- Update to the Adobe release covered by APSB26-73.
- Disable PHP execution in Magento media upload directories.
- Scan for
accesson.php, especially underassets/images/. - Review Magento
cms_blockcontent for suspicious JavaScript loaders. - Scan stores for existing shells and other signs of reinfection.
- Enable the new WAF rules to block the upload, execution, and backdoor-access stages.
AI info
This article may contain AI-generated content, but it is always reviewed and edited by a person on our team.