2026-11-05 · 5 min · Blaise
Malicious Claude Code Extension Hits Cursor
A malicious Claude Code extension on Cursor attempted to install an SSH backdoor and expose developer systems. Learn what happened and how to respond.
Malicious Claude Code Extension Hits Cursor
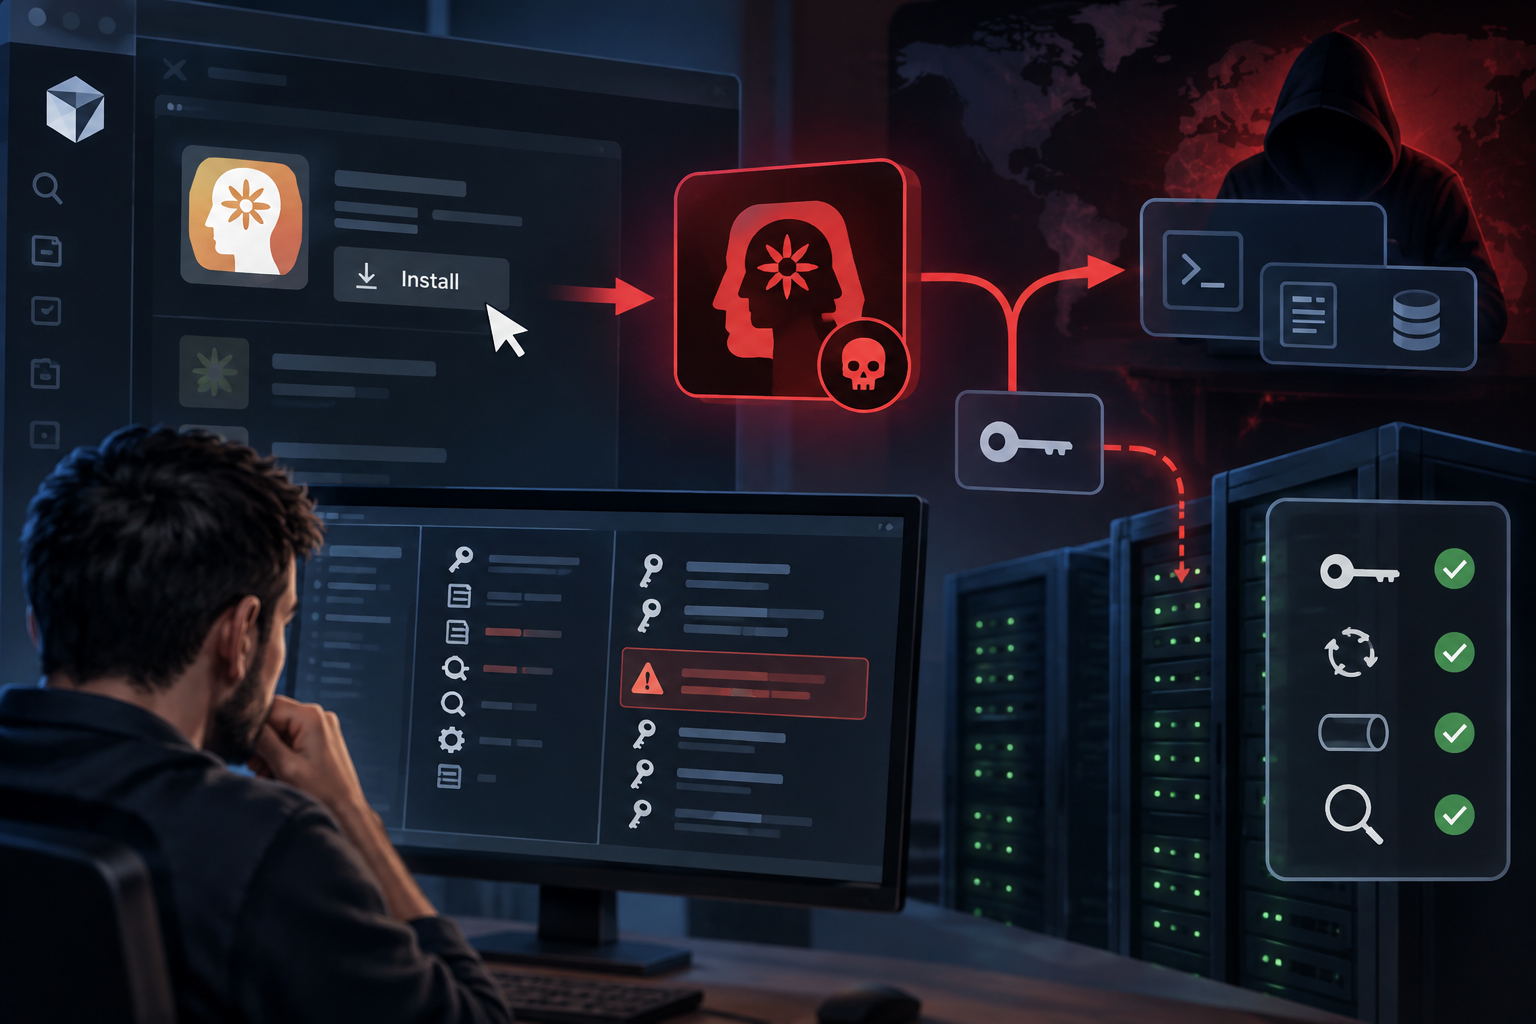
A malicious Claude Code extension was available through Cursor's VS Code extension marketplace for approximately 11 hours on October 29, 2026. The compromised versions, 2.1.312 and 2.1.313, attempted to install a persistent SSH backdoor, potentially exposing up to 5,000 developers to unauthorized access.
Cursor reported that the malicious extension was distributed between 2:27 AM and 1:35 PM Pacific Time. The company subsequently removed the affected versions, took its marketplace offline for an audit, rotated access keys, and worked with the hosting provider to disable the attacker's server.
How the Malicious Claude Code Extension Created Access
Researchers discovered a malicious JavaScript loader inserted at the beginning of the extension's extension.js file. The legitimate extension code remained intact, making the compromised package appear normal during a quick review.
The malicious code executed automatically when the extension loaded. Users did not need to interact with Claude Code to trigger it.
The loader attempted to:
Collect usernames, hostnames, Git email addresses, public IP addresses, and other system information.
Add an attacker-controlled SSH key.
Enable SSH access where possible.
Establish a reverse SSH tunnel to
134.209.82.225.Create persistence through a macOS LaunchAgent or a Windows scheduled task or Startup script.
Retry the tunnel connection approximately every minute.
The malware also searched for environment variable names associated with sensitive credentials. According to the research findings, it collected variable names rather than directly stealing the credentials stored in them.
However, this reconnaissance could have helped attackers identify valuable targets after gaining access.
Why the SSH Backdoor Did Not Work Everywhere
Coding errors limited the attack's effectiveness on many Windows and macOS systems.
On macOS, the extension checked Remote Login using systemsetup -getremotelogin without elevated privileges. The resulting administrator error prevented the malware from correctly detecting whether SSH was disabled, causing it to skip the activation step.
On Windows, the malware attempted to install and start OpenSSH through /bin/sh. This Unix shell is not available on standard Windows installations, causing the setup to fail.
Despite these limitations, the extension could still add SSH keys, create persistence mechanisms, and attempt reverse tunnel connections.
If an SSH service was not already running, however, the tunnel could not provide remote access. The failed backdoor could still leave host information exposed to the attacker's server.
What Hosts Should Check After the Malicious Extension Incident
If your team installed an affected extension during the exposure window, treat the development workstation and any connected management environment as potentially exposed.
Cursor identified an SSH key named svc-telemetry as an important indicator of compromise.
For managed servers and administration systems, review:
Authorized SSH keys: Look for unfamiliar entries, especially
svc-telemetry, or keys added during the exposure period.SSH configuration: Investigate service status and configuration changes that cannot be associated with approved maintenance.
Persistence mechanisms: Check LaunchAgents on macOS, along with scheduled tasks and Startup entries on Windows.
Outbound connections: Look for repeated SSH connections or reverse tunnel attempts to unfamiliar infrastructure.
Network logs: Search historical network and firewall logs for connections to
134.209.82.225.System reconnaissance: Investigate unexpected reports containing hostnames, usernames, public IP addresses, Git email addresses, or environment variable names.
Administrative changes: Review developer account activity affecting SSH, persistence, or remote administration.
The extension's persistence mechanisms could retry connections regularly. Therefore, a single failed connection does not rule out an affected host.
Review historical logs where available, since the attacker's server was taken offline after discovery and current connection attempts may no longer succeed.
Response Steps for Confirmed Exposure
Isolate affected systems from management networks and the internet while preserving relevant logs.
Remove unauthorized SSH keys and persistence mechanisms only after collecting the evidence needed for investigation.
Rotate secrets that were accessible from the affected environment, invalidate active sessions, and rebuild compromised systems from trusted backups when the investigation confirms an impact.
Also review systems administered from the affected workstation.
A developer endpoint may contain SSH keys, cloud credentials, Git access, or other routes into hosting infrastructure. Those systems should be investigated separately rather than assuming that a failed reverse tunnel means the wider environment was safe.
For further guidance on protecting server against unauthorized access, read our article on 5 Tips for Securing Your cPanel Server, which covers practical security measures for strengthening server access and reducing potential vulnerabilities.
You can also explore our article on PHP2Shell attacks and why BitNinja is the best defense to learn how attackers exploit vulnerabilities to execute malicious code and compromise server environments.
Lessons for Extension Marketplace Security
The incident demonstrates why extension marketplaces require the same security attention as package repositories.
A package can retain legitimate files and branding while adding a malicious loader that executes as soon as a development tool starts.
Organizations should monitor the effects of installed extensions, including SSH key modifications, new persistence entries, and unexpected outbound connections, rather than relying exclusively on an extension's name or publisher.
For additional technical details, see Cursor's official security notice and Microsoft Security Research's technical analysis.
AI info
This article may contain AI-generated content, but it is always reviewed and edited by a person on our team.