2026-11-11 · 5 min · Daniel Lendvai
Fake Gift Card Scams: How They Work & Hosting Steps
Learn how fake gift card scams trick users, abuse web hosting infrastructure, and what security steps hosting providers must take to stop them.
Fake Gift Card Scams: How They Work (And How Hosting Providers Can Stop Them)
Fake gift card scams are using familiar brands to make fraudulent reward pages look legitimate. According to a report from BleepingComputer, CTM360 identified more than 1,000 incidents involving campaigns that impersonated brands including PlayStation, Sephora, SHEIN, Walmart, and Amazon.
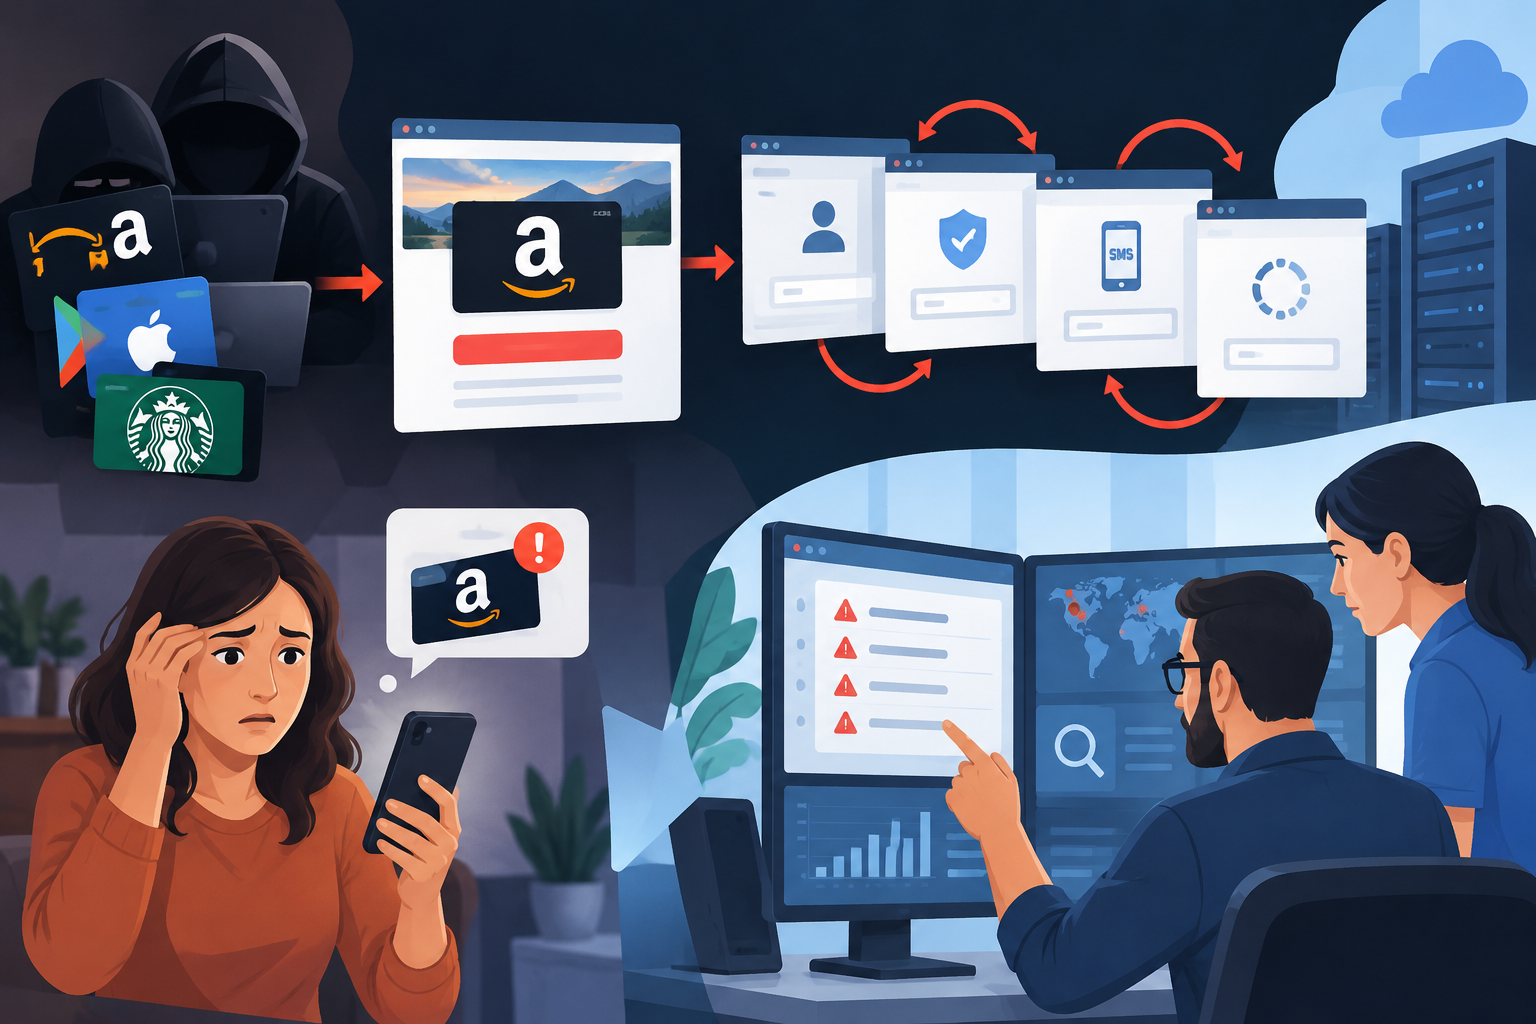
The campaigns promise a free gift card after a user clicks an advertisement and completes a quick human verification step. The reward never arrives. Instead, the victim is sent through surveys, promotional offers, application installs, browser extension installs, or paid mobile subscriptions.
For web hosts and sysadmins, these campaigns create immediate risks. Attackers frequently use compromised user accounts, hijacked subdomains, and malicious redirect scripts. Check out our web hosting security resources to protect your infrastructure.
How the scam works
The campaign starts with distribution through sponsored social media ads, viral giveaway posts, or fabricated endorsements involving celebrities and influencers. The lure sends the visitor to a fraudulent reward portal.
These pages commonly use:
- Copied brand logos, colors, and promotional language
- Fake participant numbers and countdown timers
- Fabricated testimonials from supposed winners
- A gift card value selector
- A visual animation that claims to generate the card
- A partially masked code, such as
XXXX-XXXX-7F3A-XXXX
The masked code is used to create the impression that a real reward is waiting. Before the user can see the full code, the site presents a security check or human verification gate.
That gate is the monetization step. The user is redirected to third-party offers and may be asked to submit a mobile number, enter a PIN or one-time password, complete a survey, or install software. After each task, the page reports that verification is incomplete and sends the user to another offer. CTM360 reported that no gift card was delivered in the flows it tested.
Indicators hosting teams can check
Brand impersonation is often visible in the page itself. Review reported domains and customer content for combinations of the following signs:
- A domain or subdomain using a trusted brand name without an apparent relationship to that brand
- Brand logos and colors copied into a giveaway or reward page
- Claims that a gift card can be generated after a short verification process
- Fake live counters, countdown timers, or winner testimonials
- A masked gift card code shown before a verification step
- Redirects to surveys, offers, app downloads, or paid mobile services
- Repeated requests for phone numbers, PINs, or one-time passwords
- Affiliate parameters such as
offer_idoraff_idin redirect URLs - Pages that keep sending users to new tasks after a completed action
A single indicator may have an innocent explanation. Several of these elements appearing together should trigger a closer review, especially when the page is hosted on an account that does not normally publish promotional content.
Why Compromised Accounts and Infrastructure Matter
Scam operators run modular campaigns. They rotate brand assets, target demographics, and entry domains while keeping the underlying redirect infrastructure intact.
This makes continuous account and directory monitoring essential. A sudden new directory containing stolen brand graphics, obfuscated JavaScript, or unexpected .htaccess rewrite rules is a clear sign of account compromise.
When responding to an incident, remember that the visible giveaway page is rarely the whole story. Compromised accounts often contain hidden backdoors, secondary redirect scripts, or staged payloads designed to restore the scam after a partial cleanup.
The risk to customers and brands
Victims may expose personal information, receive unexpected mobile charges, install unwanted software, or face increased spam. The impersonated brand can suffer reputational damage even when its systems were not involved.
The campaign also shows why hosting abuse teams need to look beyond credential theft. These pages are built around affiliate conversions. CTM360 observed tracking links that connect a victim's registration to an affiliate network account. When a victim completes a mobile subscription flow, the operator can earn a commission.
Practical response steps
When a suspected fake gift card page is found on a hosted account:
- Preserve the page URL, redirect chain, relevant files, and timestamps.
- Check whether the content is limited to one page or appears in other directories and domains on the account.
- Review recent account changes for unfamiliar uploads, scripts, users, or configuration changes.
- Inspect outbound links and redirect parameters, including
offer_idandaff_idvalues. - Restrict or suspend the abusive content according to the provider's abuse process.
- Contact the customer with the evidence and recommend credential resets and malware checks if compromise is suspected.
- Continue monitoring the account for replacement pages or new redirect paths.
Hosting teams should treat an apparent giveaway page as a possible account security issue, not only as a copyright or branding complaint. The combination of copied branding, fake reward generation, and endless verification provides a clear pattern for triage. Learn how automated protection tools like BitNinja Server Security detect and block malicious script injections in real time.
Source: BleepingComputer
AI info
This article may contain AI-generated content, but it is always reviewed and edited by a person on our team.