2026-11-09 · 7 min · Mark Bacsko
When a server security tool’s update channel is hijacked: 2026 cPGuard incident
The November 2026 cPGuard incident shows how a compromised update path can turn trusted root access into a supply-chain breach.
The November cPguard incident
If your servers ran one of the affected cPGuard versions, you don't have to handle the cleanup alone. Our team is happy to help you check for the indicators of compromise, we're offering a free 2-month BitNinja subscription to every hosting provider and server owner hit by this incident. Just contact us and mention this post, and we'll get you set up.
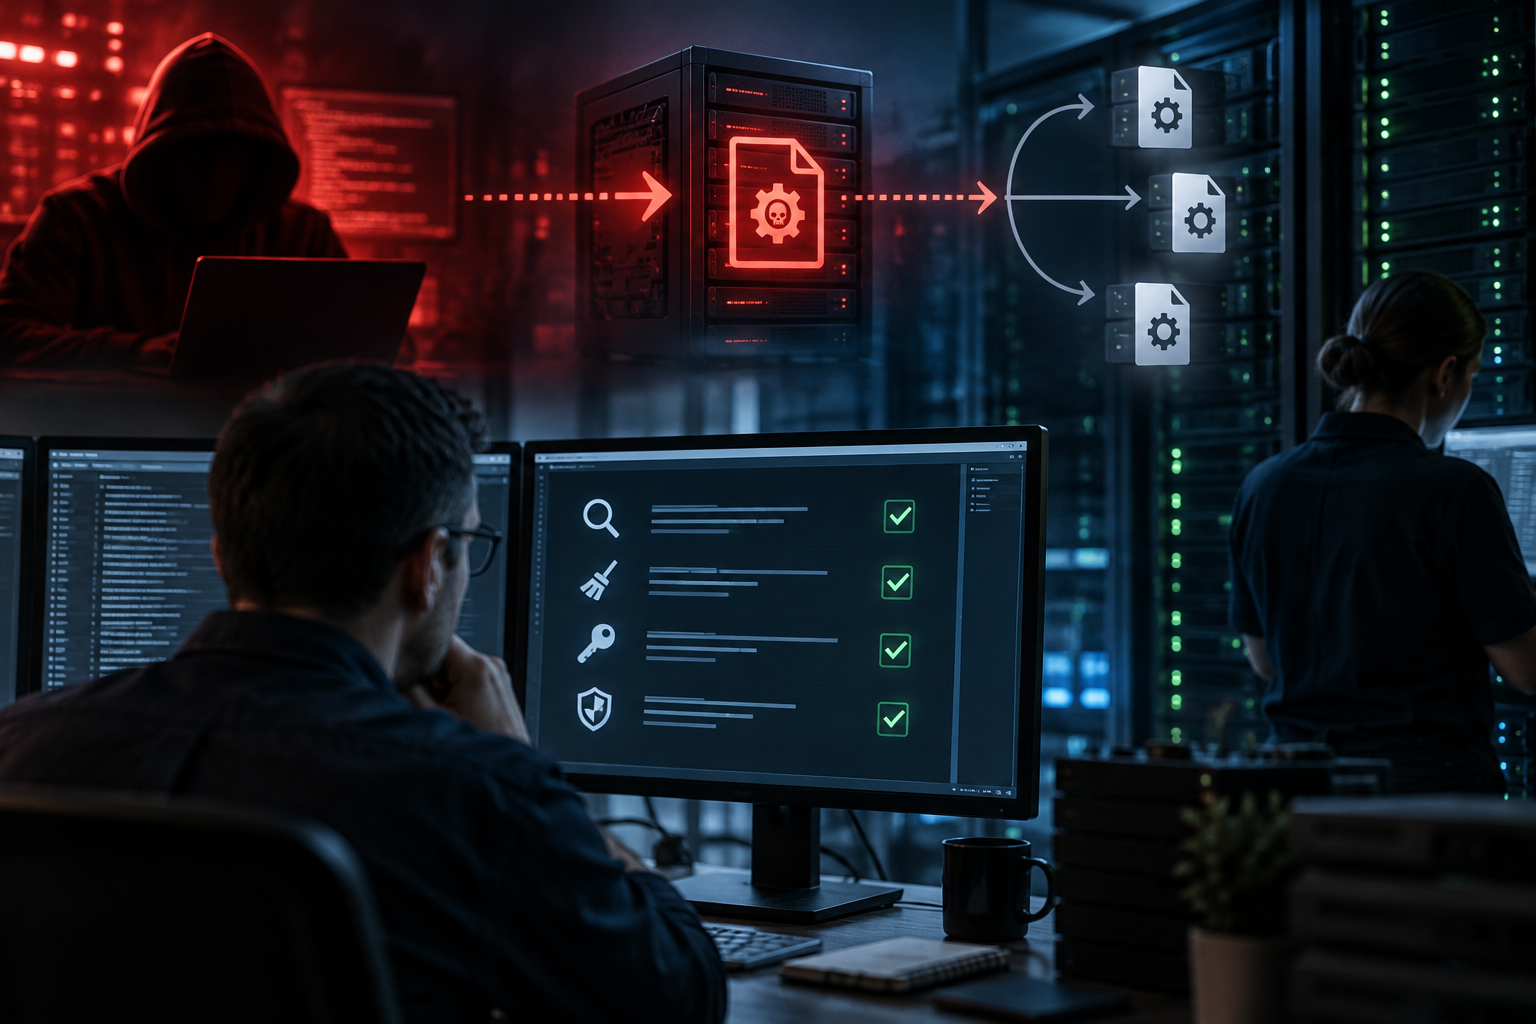
On 2 November 2026, an attacker used stolen credentials to push malicious cPGuard packages through the product’s official update channel. The affected versions were 5.88.12 through 5.88.19, distributed between roughly 02:04 and 02:09 UTC.
The updates ran with root privileges on customer servers. They installed a backdoor and collected sensitive files, including /etc/shadow, /etc/passwd, root MariaDB or MySQL configuration, root shell history, and root SSH authorization and known-hosts material. According to OPSSHIELD’s later disclosure, about 2,950 hosting servers ran the script.
This is the central supply-chain lesson: when a security tool has root access and automatic updates, its update infrastructure becomes part of the security boundary. If that channel is compromised, the attacker can reach every server that trusts the updater. On a shared hosting server, that can place many customer sites and service credentials in the same incident scope.
Why privileged update channels need separate controls
Security agents need elevated privileges to inspect files, clean malware, manage firewall rules, and perform other server-level tasks. Those privileges also make the agent and its delivery system valuable targets.
A package that arrives through an official channel may receive more trust than a normal application update. Administrators usually run it without manual review. That trust is useful for operations, but it also creates concentration risk.
The incident reinforces several controls that should apply to any privileged server agent:
- Verify package signatures and release metadata before installation.
- Protect signing keys and update credentials separately from the distribution infrastructure.
- Keep update infrastructure isolated from customer-facing systems where possible.
- Record update history centrally, so administrators can identify affected hosts even if local logs are incomplete.
- Maintain access controls outside the agent itself, including SSH restrictions, credential rotation procedures, and independent monitoring.
On 8 November 2026, cPGuard 5.89.00 moved update delivery to a privately signed channel on isolated infrastructure. The new process includes signed release metadata and SHA-256 package verification. These changes address the integrity of the delivery path, while administrators still need to handle credentials that may have been exposed before cleanup.
What hosting teams should do
The vendor’s corrective releases, 5.88.25 and 5.88.26, remove the known backdoor and staged files. The current 5.89.x releases should be preferred where they are available and supported.
Updating alone is not enough for a server that installed an affected version. Use the following process across the fleet.
1. Update and verify every server
Update every affected cPGuard installation to 5.88.25, 5.88.26, or later. Prefer the current 5.89.x release where possible. Then verify the installed version and retain the result in your fleet records.
The presence of an affected version in update history means the server installed a package from the compromised range.** It does not prove by itself that the malicious script executed**, however given the nature of the infection, it is recommended to treat any server as potentially infected, that had the update downloaded. A missing or incomplete log also does not prove that the server was unaffected.
2. Check for known indicators
Review affected systems for the indicators identified in the vendor guidance, including:
/etc/cron.d/i93677
/var/tmp/.i93677/
/var/tmp/.cpg91511_sh
/var/tmp/.cpg91511/
The corrective update removes known backdoor and staging files. Their absence after cleanup does not prove that the script never ran. Treat update history, system logs, file timelines, and other available telemetry as separate evidence sources.
3. Assume credentials may need to be replaced
A server that installed versions 5.88.12 through 5.88.19, or may have run the script, should be treated as potentially compromised.
From a trusted recovery environment:
- Reset the root password and passwords for other local accounts that can authenticate with passwords.
- Change any password reused on another system.
- Rotate MySQL and MariaDB passwords.
- Replace secrets found in root configuration files or root shell history, including applicable API tokens and storage credentials.
- Replace SSH private keys stored under
/root/.ssh. - Remove the matching old public keys from every system that trusts them.
- Review
authorized_keysfiles for unexpected entries. - Review cron entries for persistence or scheduled commands that the security agent did not create.
The files collected by the script included /etc/shadow, which contains password hashes rather than plaintext passwords. Strong hashing and unique passwords reduce the chance of offline recovery, but they do not remove the need for password resets after possible exposure. Configuration files and shell history can contain credentials in a directly usable form, so they require particular attention.
4. Review account access around the product
Follow the vendor’s account hygiene guidance where it applies. This includes resetting the billing or portal password and enabling two-factor authentication. Also review support access, API credentials, deployment accounts, and any automation that could have been reached from the affected servers.
5. Decide whether a rebuild is necessary
The vendor’s published guidance does not recommend a full operating system rebuild as the routine response. It recommends updating the agent and completing credential resets and rotations.
A rebuild may still be appropriate when additional compromise indicators are present, server integrity cannot be established, or the team cannot confidently remove persistence and replace exposed credentials. Make that decision using the evidence available for each host rather than applying the same answer to the entire fleet.
Defense in depth for privileged agents
A root-level security agent can be an important control, but it should not be the only control protecting a hosting server. Independent layers give administrators a way to detect or contain a problem if the agent, its update channel, or its credentials are compromised.
Useful layers include centralized authentication logs, file and process monitoring, restricted SSH access, separate management networks, tested backups, least-privilege service accounts, and an incident process that covers credential rotation. Fleet-wide update records are especially valuable during a supply-chain event because local cleanup can remove the very files investigators need to identify.
Hosting providers should also define how a privileged agent is allowed to update. That policy can include release verification, staged deployment, canary servers, rollback procedures, and an approval path for unusual version changes. These controls add operational work, but they limit the number of systems exposed by a bad release.
For this incident, the immediate fleet check is clear:
- Identify servers that installed cPGuard 5.88.12 through 5.88.19.
- Update them to a fixed current release.
- Check the known indicators and relevant logs.
- Reset and rotate credentials from a trusted environment.
- Replace exposed SSH keys and remove old trust relationships.
- Review cron,
authorized_keys, portal access, and support access. - Escalate hosts with unexplained activity or uncertain integrity for individual assessment.
The broader operational requirement applies to any security tool with root access: verify the update path, keep independent controls in place, and treat cleanup and credential rotation as separate tasks.
Sources:
https://opsshield.com/notice/cpguard-update-channel-compromise.html
https://www.bleepingcomputer.com/news/security/hackers-hijack-cpguard-autoupdate-to-deploy-backdoor-steal-data/
AI info
This article may contain AI-generated content, but it is always reviewed and edited by a person on our team.